Services
Products
Website IntelligenceLive analytics, chat & leads
Hotels & ResortsNewFront desk, bookings & compliance
Messaging for ResellersPartnerSell SMS & WhatsApp as your own
People & HRHiring to exit, one portal
Privacy TrainingNewDPDP Act training for teams
All products
About us Clients Our approach Contact
Book a free consultation +1 510-421-6849
Compliance, Risk & Governance

Best GDPR Data Protection Compliance Services in the US

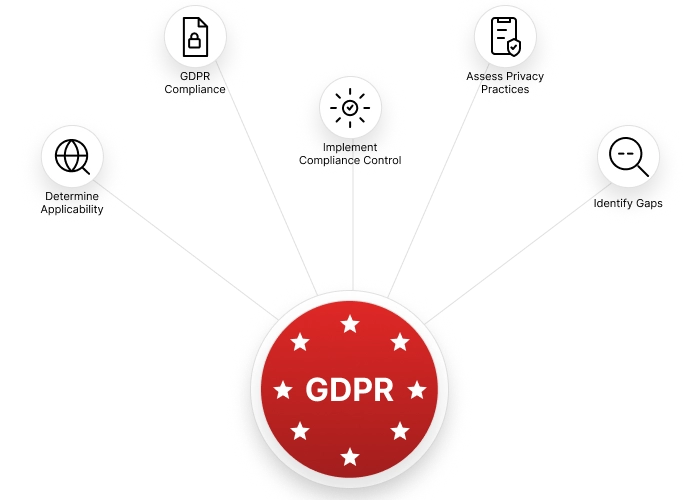
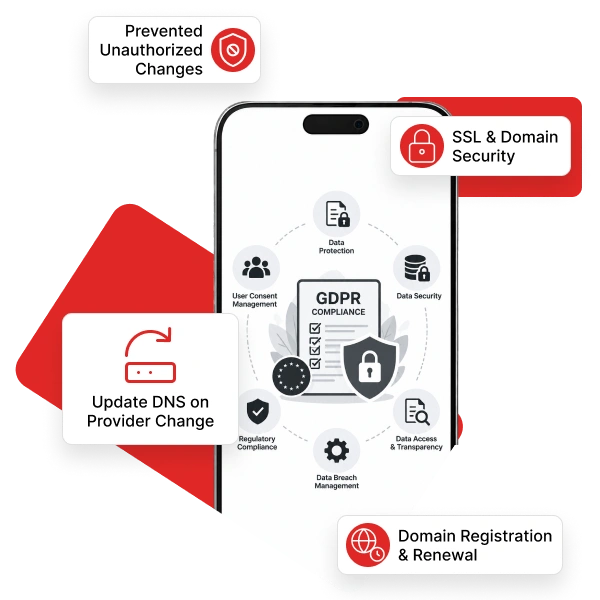
We provide GDPR compliance services for US businesses that collect, process, or manage personal data connected to individuals in the European Union. Our services help organizations determine whether GDPR applies, assess privacy practices, identify gaps, and implement practical compliance controls.

GDPR compliance services covering privacy, data protection and regulatory needs worldwide
Standards and technologies
  • GDPR Compliance Assessment
  • Data Mapping
  • DPIA
  • Consent & Rights
  • Privacy Notices
  • Vendor Compliance
  • Data Transfers
Challenges

Why GDPR Compliance Matters for US Businesses

GDPR compliance helps organizations protect personal data and manage privacy risks

GDPR Compliance Challenges

US businesses may need to address GDPR when they:

  • Offer products or services to EU customers
  • Monitor EU users or their online behavior
  • Process personal data of individuals in the EU
  • Work with EU customers, vendors, or business partners

Common challenges include:

  • Incomplete data mapping
  • Unclear lawful basis
  • Weak consent processes
  • Outdated privacy notices
  • Limited data subject rights procedures
  • Unclear third party data processing
Risks of Poor GDPR Preparation

Poor management can lead to:

  • Privacy compliance gaps
  • Delays in responding to data subject requests
  • Weak data protection practices
  • Vendor and transfer risks
  • Regulatory exposure
  • Challenges with EU customer contracts

Xcodefix Global helps US organizations determine whether GDPR applies, identify privacy gaps, and implement practical controls across data mapping, consent, privacy notices, DPIAs, rights management, vendors, and data transfers, while also considering DPDP privacy compliance where applicable

Have more questions?

Our specialists are here to help. Contact Xcodefix Global today.

contact us
Overview

When Does GDPR Apply to US Organizations?

GDPR may become relevant to a US organization when its activities involve individuals in the EU.

GDPR Impact Assessment and Compliance Services

Serving EU Customers

Businesses offering products or services to customers in the EU may need to assess GDPR applicability and related privacy obligations.

GDPR Compliance Monitoring and Privacy Services

Monitoring EU Users

Websites, applications, and digital platforms that monitor or analyze the behavior of individuals in the EU may need to evaluate GDPR requirements.

GDPR Data Storage and Processing Compliance Services

Processing EU Personal Data

US organizations may process EU personal data through customer accounts, employee records, marketing activities, analytics, or business operations.

GDPR Compliance Implementation and Support Services

Working With EU Businesses

US companies working with EU customers, partners, vendors, or processors may need appropriate privacy agreements and data protection controls.

In practice

GDPR Compliance Assessment Areas

Assessment AreaWhat We Review
Regulatory ApplicabilityGDPR requirements relevant to your business activities and processing
Data MappingPersonal data, processing purposes, data flows, recipients, and retention
Privacy GovernancePolicies, roles, accountability, ROPA, and governance processes
Lawful Basis & ConsentLawful basis, consent, withdrawal, and transparency
Data Subject RightsAccess, correction, erasure, objection, and request handling
Privacy RiskDPIAs, privacy risks, and risk treatment
Vendors & TransfersProcessor controls, contracts, and international data transfers
Breach ResponseIncident assessment, documentation, escalation, and notification procedures
Services

GDPR Compliance Services We Provide in the US

GDPR Applicability Assessment

We assess your business activities and data processing to determine where GDPR requirements may apply.

GDPR Gap Assessment

We compare existing privacy practices, policies, processes, and controls against applicable GDPR requirements.

Data Mapping & ROPA

We help document personal data, processing activities, data flows, recipients, retention, and processing purposes.

Privacy Notices & Consent Management

We review privacy notices, consent processes, lawful basis documentation, and consent withdrawal procedures.

DPIA & Privacy Risk Assessment

We support DPIAs and privacy risk assessments for processing activities that may create higher risks to individuals.

Data Subject Rights Management

We help establish processes for handling GDPR requests, including access, correction, erasure, objection, and portability requests.

Vendor & Processor Compliance

We review third party processing, data processing agreements, vendor controls, and privacy responsibilities.

International Data Transfer Compliance

We assess international data transfers and help organizations identify appropriate contractual and technical safeguards.

Breach Response & Notification Readiness

We help establish privacy breach procedures that support incident assessment, documentation, escalation, and applicable notification requirements.

In depth

GDPR Compliance Areas We Review in the US

GDPR compliance requires more than maintaining a privacy policy. We review the operational practices supporting personal data protection across:

  • Data Mapping & Processing Records: Data inventories, processing purposes, data flows, retention, recipients, and ROPA where applicable.
  • Lawful Basis & Consent: Lawful bases, consent mechanisms, consent withdrawal, transparency, and consent management.
  • Privacy Notices & Policies: Privacy notices, internal policies, data minimization, purpose limitation, and transparency.
  • Data Subject Rights: Access, correction, erasure, objection, portability, and rights request handling.
  • DPIA & Privacy by Design: DPIAs, privacy risk assessments, and privacy considerations within products and processes, and OWASP Secure Code Review
  • Vendor & Processor Compliance: Processor obligations, third party access, contracts, and vendor reviews.
  • Breach Response & Transfers: Breach procedures, notification requirements, international transfers, and applicable safeguards.
  • Privacy Governance: Accountability, privacy roles, documentation, and governance processes supported by ISO 27001 / 22301 Consulting.

We assess these areas against applicable GDPR requirements and identify gaps requiring attention.

Process

How Our GDPR Compliance Process Works in the US

Plan your project
  1. 1

    Determine Applicability & Scope

    We review your business activities, customers, markets, and processing activities to identify relevant GDPR requirements.

  2. 2

    Map Personal Data

    We identify what personal data you collect, where it comes from, how it is used, where it is stored, and who receives it.

  3. 3

    Identify Compliance Gaps

    We assess existing privacy controls, policies, processes, and documentation against applicable GDPR requirements.

  4. 4

    Prioritize Remediation

    We identify key privacy risks and establish practical remediation priorities.

  5. 5

    Implement Privacy Controls

    We support improvements to privacy notices, consent, rights handling, DPIAs, vendor controls, and data transfer processes.

  6. 6

    Maintain GDPR Readiness

    We support periodic reviews, regulatory updates, evidence management, and ongoing privacy governance.

GDPR Compliance Timeline: The time required for a GDPR compliance programme depends on the scope of processing, number of systems and vendors, existing privacy controls, and remediation needs. A focused gap assessment may take less time, while larger programs require more time for data mapping, control implementation, and remediation.

Use cases

GDPR Compliance Use Cases We Support in the US

International SaaS Companies

Privacy compliance for US businesses serving EU customers and markets.

US Based Organizations

GDPR requirements for international customers, users, and data processing.

Growing Technology Companies

Practical privacy controls as products, systems, and data processing expand.

First Time Privacy Programmes

Applicability assessment, data mapping, gap analysis, and compliance implementation.

Organizations Operating Across Jurisdictions

Coordinated GDPR compliance for US businesses with EU operations or customers.

Organizations Maintaining Compliance

Ongoing reviews, regulatory updates, privacy controls, and operational processes.

Example

Practical GDPR Compliance Example

A US based SaaS company served customers across the EU but lacked complete visibility into its personal data flows and third party processing

We reviewed its processing activities, mapped personal data across applications and vendors, and assessed privacy notices, consent, data subject rights, retention, and international transfers.

The assessment identified key gaps and provided a clear remediation plan for improving GDPR readiness.

Why Xcodefix

Why Xcodefix Global for GDPR Compliance Services?

GDPR Privacy Compliance and Data Protection Services

US Focused GDPR Expertise

We help US businesses understand when GDPR may apply and what controls they need to address applicable requirements.

GDPR Privacy Impact Assessment and Compliance

Practical Privacy Assessments

We focus on actual data flows, systems, vendors, and business processes instead of treating GDPR as a documentation exercise.

GDPR Data Security and Compliance Support Services

Security & Privacy Alignment

We connect privacy requirements with security controls, access management, breach response, and data protection practices.

GDPR Data Engineering and Privacy Compliance Services

Data and Engineering Awareness

We design practical privacy controls that work with existing products, applications, and operational workflows.

Ongoing GDPR Compliance Monitoring and Support

Ongoing Compliance Support

We support remediation, privacy reviews, data mapping updates, rights processes, vendor assessments, and ongoing GDPR readiness.

Coverage

Nationwide GDPR Compliance Services Across the US

We offer GDPR compliance solutions for companies in the United States in various sectors such as SaaS, health tech, eCommerce, financial services, and technology. We help firms assess GDPR compliance requirements, discover areas that need improvement concerning privacy, enhance controls, and remain compliant.

  • California
  • Texas
  • Florida
  • New York
  • Illinois
  • Pennsylvania
  • Ohio
  • Georgia
  • North Carolina
  • Washington
  • Virginia
  • Massachusetts
  • Arizona
  • Colorado
  • Michigan
  • Minnesota
  • New Jersey
  • Tennessee
  • Maryland
Get Started

Assess Your GDPR Compliance Readiness

Understand whether GDPR applies to your US business and identify the privacy controls that need attention.

Prefer email? info@xcodefixglobal.com

Get a Free Consultation

Fields marked with an asterisk are required.

A few sentences is enough — we'll ask follow-up questions.

We use your details only to reply. See our privacy policy.
Frequently asked questions

Common Questions About GDPR Compliance for US Businesses

Talk to the specialist who would scope the work — not a call-centre script.

Ask us directly

Does GDPR apply to US companies?

GDPR may apply to US companies that offer goods or services to individuals in the EU or monitor their behavior. Applicability depends on the organization’s activities and data processing.

How can a US company determine if GDPR applies?

We review the company’s customers, markets, products, data subjects, processing activities, and monitoring practices to determine whether GDPR requirements may apply.

Does having EU customers automatically make a US company subject to GDPR?

Not necessarily. GDPR applicability depends on the nature of the company’s activities and processing. An applicability assessment can help determine whether the regulation applies.

What does a GDPR compliance assessment include?

It can include applicability, data mapping, ROPA, lawful basis, consent, privacy notices, data subject rights, DPIAs, vendors, data transfers, breach response, and privacy governance.

Does a US company need a GDPR Data Protection Officer?

A DPO is required only in specific circumstances under GDPR. We assess the organization’s processing activities and regulatory obligations to determine whether a DPO requirement may apply.

Can Xcodefix help with GDPR data subject requests?

Yes. We help establish processes for receiving, verifying, reviewing, responding to, and documenting applicable GDPR data subject requests.

Does GDPR require US companies to stop transferring data to the US?

No. GDPR does not generally prohibit international data transfers. However, organizations must address applicable transfer requirements and safeguards.

Can Xcodefix support ongoing GDPR compliance?

Yes. We provide ongoing support for privacy reviews, data mapping, remediation, rights processes, vendor assessments, and updates to privacy controls.