Services
Products
Website IntelligenceLive analytics, chat & leads
Hotels & ResortsNewFront desk, bookings & compliance
Messaging for ResellersPartnerSell SMS & WhatsApp as your own
People & HRHiring to exit, one portal
Privacy TrainingNewDPDP Act training for teams
All products
About us Clients Our approach Contact
Book a free consultation +91 95003 00734
Compliance, Risk & Governance

ISO 27001 Consultant for Malaysian Organizations, Working Remotely

For Malaysian organizations building or rebuilding an ISMS to ISO/IEC 27001:2022, whether a 2013 certificate lapsed at the October 2025 cutoff or the amended PDPA, NACSA or Bank Negara now asks for more. We design the ISMS so its controls produce the evidence those regimes expect. Our consultants work from Coimbatore and Chennai, India, two and a half hours behind Kuala Lumpur.

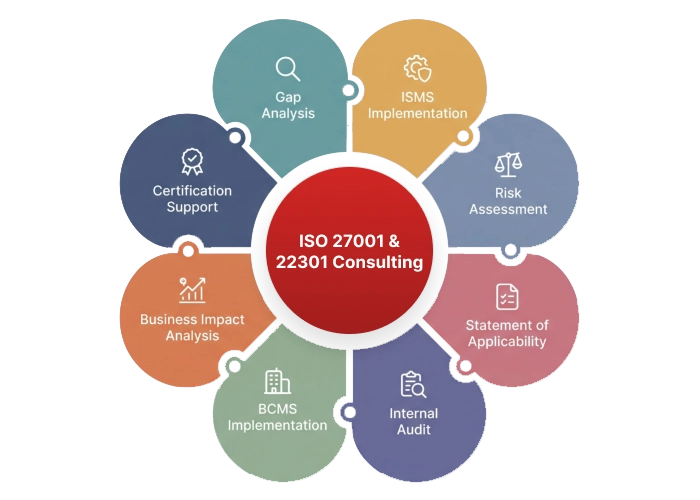
ISO 27001 consulting cycle covering gap analysis, ISMS implementation, risk assessment, Statement of Applicability, internal audit and certification support
Standards and technologies
  • ISO/IEC 27001:2022
  • PDPA Amendment 2024
  • Cyber Security Act 2024
  • BNM RMiT
  • Standards Malaysia
  • Annex A
Challenges

Where Malaysian ISO 27001 Programs Stand in Late 2026

Three things changed for Malaysian ISMS owners in two years: the 2013 edition reached the end of its life, the PDPA gained breach notification and DPO duties, and critical infrastructure got its own Act. An ISMS designed before those changes probably does not reflect them.

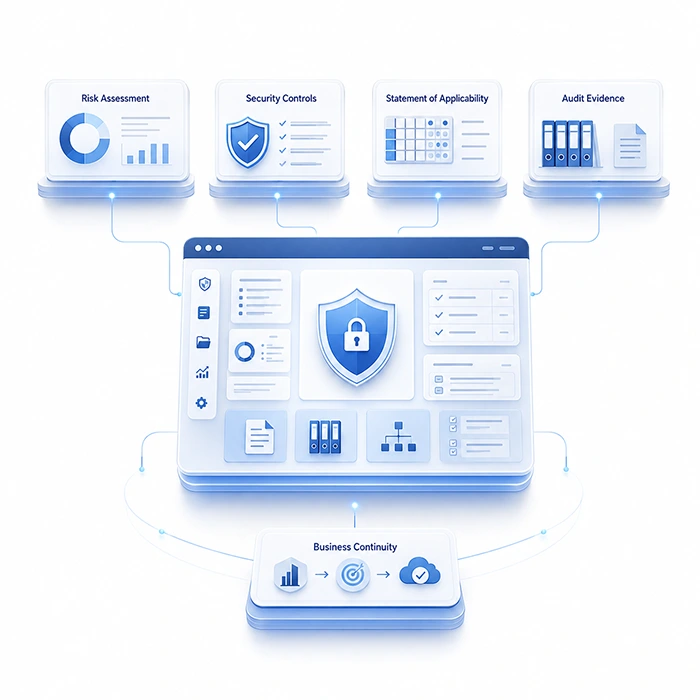
ISMS workspace connecting risk assessment, security controls, the Statement of Applicability and audit evidence

What Changed

  • IAF set 31 October 2025 as the end of the transition; certificates to ISO/IEC 27001:2013 expired or were withdrawn after that date
  • The Personal Data Protection (Amendment) Act 2024 came into force in stages, the last on 1 June 2025
  • The Cyber Security Act 2024 has applied to NCII entities since 26 August 2024
  • Bank Negara Malaysia's RMiT policy was replaced by a version effective 28 November 2025

Where Projects Go Wrong

  • A Statement of Applicability copied from a template, with no link to the risk register
  • Breach procedures that know nothing of the PDPA's 72-hour notice or the six-hour NCII notice
  • Supplier controls that ignore the PDPA's new direct duties on data processors
  • A certificate from a body that is not accredited, which a regulator or customer may question
  • Policies on file but no internal audit or management review on record

We are consultants, not a certification body. We build the ISMS and prepare you for the audit; an accredited certification body decides. Our ISO 27001 certification consulting covers gap analysis, risk treatment, the Statement of Applicability, documentation and internal audit. Malaysian engagements are handled online by consultants based in Coimbatore and Chennai, India. There is no Malaysian office.

Did your 2013 certificate lapse?

Tell us when it expired and which body certified you. A consultant will reply by the next business day with a route back to certification.

contact us
Overview

Malaysian Requirements Your ISMS Has to Carry

ISO/IEC 27001 asks you to identify the legal and regulatory requirements that apply to you. In Malaysia in 2026, that list is longer than it was.

Certificate with a star rosette representing Standards Malaysia accredited certification bodies

Accreditation by Standards Malaysia

Standards Malaysia accredits ISMS certification bodies under its Accreditation of Certification Bodies scheme. On 1 November 2026 its directory listed four: SIRIM QAS International, CyberSecurity Malaysia, BSI Services Malaysia and NIOSH Certification. It has been an IAF MLA signatory for ISO/IEC 27001 since July 2017, the arrangement through which accreditation is recognized between countries.

Person holding a shield representing Malaysia's amended PDPA

PDPA Amendments of 2024

Act A1727 took effect in three stages. From 1 April 2025, data processors must meet the Security Principle directly, biometric data became sensitive personal data, and the maximum penalty rose to RM1 million or three years. From 1 June 2025, controllers must notify breaches, appoint a data protection officer and act on data portability requests.

Two speech bubbles with arrows representing PDPA breach notification

Breach Notice and the DPO

The Commissioner's guideline requires notice within 72 hours of a breach that causes or is likely to cause significant harm, including any affecting more than 1,000 people, and notice to individuals within seven days after that. A DPO is required above 20,000 data subjects, or 10,000 for sensitive data, and must be resident in Malaysia or easily contactable, and proficient in Bahasa Melayu and English.

Shield with circuit lines representing Malaysia's Cyber Security Act 2024

Cyber Security Act 2024

NCII entities in 11 sectors must carry out a cyber security risk assessment at least once a year and an audit by a NACSA-approved auditor at least every two years, report incidents immediately with particulars within six hours, and follow their sector's code of practice. NACSA's guidance asks NCII agencies to hold ISO/IEC 27001 certification or an equivalent.

Government building beside a signed document representing Bank Negara Malaysia RMiT

BNM Risk Management in Technology

RMiT, effective 28 November 2025, expects quarterly vulnerability assessments, annual intelligence-led penetration tests by suitably accredited testers, an independent compromise assessment at least every three years, an annual cyber drill, and a third-party review before critical systems first move to public cloud. Its NCII code of practice names ISO/IEC 27001:2022 among the standards a cyber security policy must align with.

ANNEX A IN MALAYSIAISO/IEC 27001:2022 Annex A vs Malaysian obligation it supports
AspectISO/IEC 27001:2022 Annex AMalaysian obligation it supports
Incident handling5.24 to 5.28: planning, assessment, response, lessons learned, evidencePDPA 72-hour breach notice; Act 854 six-hour particulars and 14-day follow-up
Privacy5.34 Privacy and protection of PIIPDPA principles, DPO appointment, data portability
Legal register5.31 Legal, statutory, regulatory and contractual requirementsA maintained list of PDPA, Act 854, RMiT and sector code duties
Suppliers and cloud5.19 to 5.23, including information security for use of cloud servicesProcessor duties under the PDPA; RMiT review before first public cloud use for critical systems
Vulnerabilities8.8 Management of technical vulnerabilitiesRMiT quarterly assessments and annual penetration tests
Independent review5.35 Independent review of information securityAct 854 audit every two years; RMiT compromise assessment
Continuity5.29 and 5.30: security during disruption, ICT readinessRMiT annual cyber drill and resilience reviews
Awareness6.3 Awareness, education and trainingRMiT annual awareness training for staff

Treat the table as a starting point. Your risk assessment decides which controls apply, and the Statement of Applicability records why, citing the Malaysian obligation where one exists. For privacy work beyond the ISMS, the data mapping, DPIA and breach procedures from our GDPR data protection compliance service carry over well to the PDPA.

Services

What We Deliver for a Malaysian ISMS

Scope and Context

A scope you can defend at Stage 1, with the context analysis that clause 4.1 now requires to consider whether climate change is a relevant issue, following Amendment 1:2024.

Risk Assessment and Treatment

A risk register built from your assets and processes, with treatment plans that name owners and dates rather than generic intentions.

Statement of Applicability

All 93 Annex A controls considered, each included or excluded with a reason tied to a risk or a Malaysian obligation.

Policies and Procedures

Only the documents the ISMS needs, including a breach procedure that runs the PDPA and NCII clocks side by side.

Internal Audit and Management Review

An internal audit against the 2022 edition and a minuted management review, both of which the certification body will ask to see.

Awareness and Incident Drills

Annex A 6.3 training through our security awareness training program, and tabletop tests of the breach procedure drawn from our incident response practice, leaving records a BNM or NACSA review can examine.

Certification Audit Support

Preparation for Stage 1 and Stage 2 with the accredited body you choose, and help closing any nonconformities afterwards.

Penetration testing and managed SOC monitoring for systems in Malaysia are licensable services under the Cyber Security Act 2024, and NACSA's licensing FAQ says a foreign company providing cyber security services to companies in Malaysia must apply for a license. ISO 27001 consulting is not a licensable service. When your risk treatment calls for a penetration test, check that the tester holds a NACSA license.

Process

How a Remote ISO 27001 Project Runs on Malaysia Time

Malaysia Time is UTC+8 with no daylight saving, and India Standard Time is UTC+5:30. Kuala Lumpur therefore runs 2 hours 30 minutes ahead: a 2:00 p.m. meeting in Kuala Lumpur is 11:30 a.m. in Chennai, and the Malaysian afternoon from noon to 6:00 p.m. sits inside a 9:30 a.m. to 6:30 p.m. Indian working day.

Plan your project
  1. 1

    Gap Assessment

    Interviews with process owners by video, booked in your afternoons, plus a document review against the 2022 edition. You get a written gap report and a plan.

  2. 2

    Risk Workshop

    A facilitated session to agree assets, threats, risk criteria and owners, recorded straight into the risk register.

  3. 3

    Build

    Policies, procedures and the Statement of Applicability drafted in a shared workspace and reviewed with your team weekly.

  4. 4

    Operate

    The ISMS runs for a period so that monitoring, incident and training records exist before anyone audits them, with staff sessions from our security awareness training where needed.

  5. 5

    Internal Audit and Review

    Our auditor checks the system against the standard; your management reviews the results and signs off.

  6. 6

    Certification

    Stage 1 and Stage 2 with your certification body, with us on call for evidence questions.

Timing: Implementation usually takes several months, because the ISMS must operate, be audited internally and be reviewed by management before the certification audit. We set the plan after the gap assessment, not before.

Use cases

Who This Fits in Malaysia

Banks and Financial Institutions

Institutions mapping RMiT expectations into one management system.

NCII Entities and Their Suppliers

Organizations in the 11 NCII sectors, and vendors whose customers now ask for evidence.

Technology Exporters

Software and IT service firms whose overseas buyers ask for ISO 27001.

Private Healthcare

Healthcare services are an NCII sector, and patient data is sensitive personal data under the PDPA.

Lapsed 2013 Certificate Holders

Companies that missed the 31 October 2025 transition and need certification to the 2022 edition.

Data Processors

Service providers now bound directly by the PDPA Security Principle.

Why Xcodefix

Why Work With Xcodefix on Your ISMS

Warning triangle representing risk-driven ISMS design

Risk Before Paperwork

Controls are chosen from your risk register, so the Statement of Applicability survives an auditor's questions.

Shield with a gear representing engineers who implement controls

Security Engineers in the Team

Findings in access control, logging or vulnerability handling can be fixed by our engineers, not just written up.

Clipboard with a checklist and pencil representing independent certification

Clear Role Separation

We never certify you. The accredited body you choose does, which keeps the certificate credible.

Checklist with a person representing combined PDPA and ISMS work

Privacy and Security Together

PDPA duties and ISO 27001 controls are designed in one program, not two.

Two people in conversation representing daily working overlap with Malaysia

Afternoon Working Overlap

Six shared hours a day for calls, with written status in your inbox each morning.

Person inside a triangle with gears representing a company founded in 2008

Since 2008

Founded in 2008, with 5,203+ clients across four continents.

ISO 27001 in Malaysia

Start With a Gap Review Against the 2022 Edition

Send us your current scope, any existing ISMS documents and the regimes you answer to: PDPA, Act 854, RMiT or customer contracts. A consultant will come back by the next business day with the gaps we would check first and a proposed plan.

Prefer email? info@xcodefixglobal.com

Request an ISMS Gap Review

Fields marked with an asterisk are required.

A few sentences is enough — we'll ask follow-up questions.

We use your details only to reply. See our privacy policy.
Frequently asked questions

ISO 27001 in Malaysia: Questions We Hear

Talk to the specialist who would scope the work — not a call-centre script.

Ask us directly
How do I get ISO 27001 certification in Malaysia?

Build and run an ISMS that meets ISO/IEC 27001:2022, carry out an internal audit and management review, then engage a certification body for a Stage 1 and Stage 2 audit. Choose a body accredited for ISMS, which you can check in Standards Malaysia's online directory. A consultant can build the ISMS with you, but only the certification body can certify it.

How much does ISO 27001 certification cost in Malaysia?

There are two separate costs: the certification body's audit fees and the effort to implement the ISMS, whether internal or consultant-led. We have not found reliable published price lists for Malaysian certification audits, so ask each accredited body for a quote based on your headcount and scope. We price implementation after a gap review.

How long does it take to get ISO 27001 certified?

Usually several months. The ISMS has to operate long enough to produce records, then pass an internal audit and management review before the Stage 1 and Stage 2 audits. A company with mature security practices and a narrow scope moves faster than one starting from scratch across several sites. We give a timeline after the gap assessment.

Is ISO 27001 certification mandatory in Malaysia?

Not for most companies. NACSA's guidance asks NCII agencies to hold ISO/IEC 27001 certification or an equivalent, and BNM's code of practice for banking NCII entities names ISO/IEC 27001:2022 among the standards a cyber security policy must align with. For everyone else, the push usually comes from customers and tenders.

Is an ISO/IEC 27001:2013 certificate still valid?

No. Under IAF's transition rules, all certifications based on ISO/IEC 27001:2013 expired or were withdrawn at the end of the transition period on 31 October 2025. An organization still holding one needs certification to the 2022 edition, which in practice means a new audit by an accredited certification body.

Do we need a data protection officer under the amended PDPA?

Since 1 June 2025, a DPO is required if you process personal data of more than 20,000 data subjects, sensitive personal data of more than 10,000, or carry out regular and systematic monitoring, according to the Commissioner's DPO guideline. Processors are covered too. The DPO must be resident in Malaysia or easily contactable, and the Commissioner must receive the DPO's contact details within 21 days of appointment.

What changed in Annex A of ISO 27001:2022?

Annex A now holds 93 controls in four themes, organizational, people, physical and technological, down from 114 in the 2013 edition. Eleven controls are new, and the set now includes controls such as 5.23 on information security for use of cloud services and 5.30 on ICT readiness for business continuity. Amendment 1:2024 also requires you to consider whether climate change is a relevant issue.

Can a consultant in India support a Malaysian ISMS?

Yes. Interviews, workshops and document reviews work well over video, and the time difference with India is only two and a half hours, so afternoons overlap fully. ISO 27001 consulting is not a licensable service under the Cyber Security Act 2024. Penetration testing for Malaysian systems is, so use a NACSA-licensed tester. Our SOC 2 page for Singapore covers the regional attestation side.