Services
Products
Website IntelligenceLive analytics, chat & leads
Hotels & ResortsNewFront desk, bookings & compliance
Messaging for ResellersPartnerSell SMS & WhatsApp as your own
People & HRHiring to exit, one portal
Privacy TrainingNewDPDP Act training for teams
All products
About us Clients Our approach Contact
Book a free consultation +91 95003 00734
Compliance, Risk & Governance

HIPAA Consultants in Bangalore for Teams Handling US PHI

For Bengaluru healthtech, SaaS, revenue cycle and IT services firms whose US clients pass them protected health information. We work out what HIPAA expects of you as a business associate, test your safeguards against the Security Rule, and fit that program alongside India's DPDP Act and the CERT-In directions you already answer to.

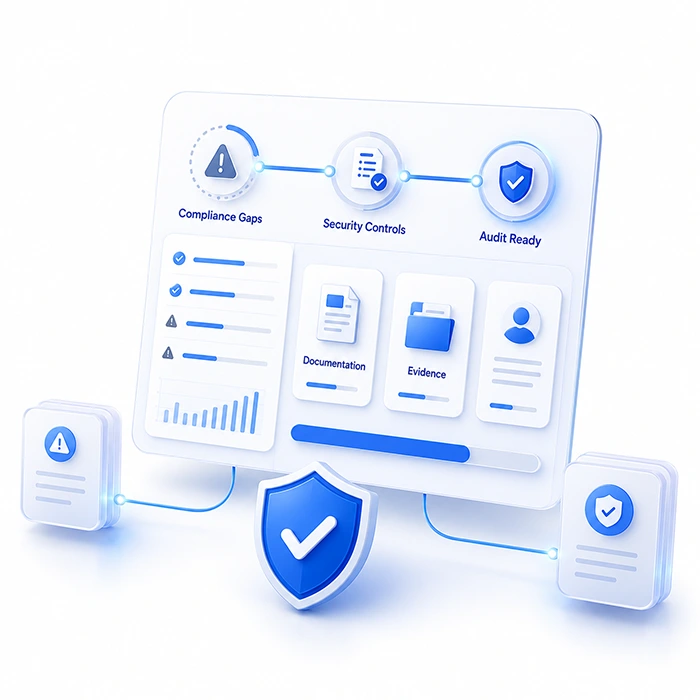
Compliance dashboard tracking control gaps, security controls, documentation and evidence for a business associate's HIPAA program
Standards and technologies
  • HIPAA Security Rule
  • Business Associate Agreements
  • 45 CFR 164.410
  • DPDP Act 2023
  • CERT-In Directions 2022
Challenges

How a Bengaluru Company Becomes a HIPAA Business Associate

HIPAA is a US law, but its reach follows the data. The test is about what you do with protected health information (PHI), not where your office is.

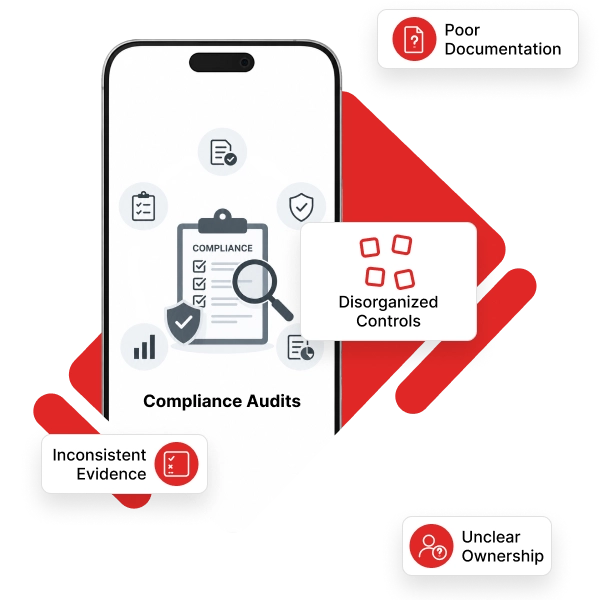
Compliance audit checklist on a phone flagged for poor documentation, disorganized controls, inconsistent evidence and unclear ownership

The definition that pulls you in

45 CFR 160.103 treats as a business associate anyone outside a covered entity's workforce who handles PHI for it, whether by creating, receiving, maintaining or transmitting it. The rule names the kind of work that qualifies: claims processing, data analysis, billing, practice management, utilization review and similar functions. That list reads like a description of Bengaluru's health-adjacent outsourcing and product work.

The chain continues downstream. If your client is itself a US vendor, the same definition makes you a subcontractor, and subcontractors that handle PHI are business associates too.
What the contract hands you

Your US client may not pass you electronic PHI until it has written assurances, which in practice means a business associate agreement (BAA). Under 45 CFR 164.314, that agreement must require you to:

  • comply with the Security Rule, which 45 CFR 164.302 also applies to business associates directly;
  • bind any subcontractor that touches the ePHI to the same terms;
  • report security incidents to the covered entity, including breaches of unsecured PHI.

For a breach, 45 CFR 164.410 sets the outer limit: tell the covered entity without unreasonable delay and no later than 60 calendar days after discovery. Your BAA may set a shorter contractual window, so read it before you write a runbook.

Our HIPAA compliance consulting practice already supports business associates serving US healthcare organizations. For a Bengaluru team, the first deliverable is usually a data-flow map that shows where PHI arrives, where it rests and which people and vendors can see it. A HIPAA risk assessment is then built on that map instead of a generic checklist.

Not sure you are a business associate?

Describe the data your US client shares with you. You will hear back within one business day.

contact us
Overview

No Official HIPAA Certification Exists. Here Is What Buyers Check

Search results for HIPAA consultants in Bangalore are crowded with certificates. HHS's own Security Rule FAQ says the rule contains no requirement to certify compliance, that HHS does not endorse or recognize private organizations' certifications, and that a certificate does not stop HHS from later finding a violation. A course certificate can document training. It is not what a US procurement team relies on.

Document icon representing a signed business associate agreement

A BAA you can actually operate

Buyers want the agreement signed, plus signs that its clauses work: a named incident contact, a tested reporting path and a current list of downstream subcontractors.

Risk gauge icon for a HIPAA Security Rule risk analysis

A current risk analysis

45 CFR 164.308 makes a thorough, accurate risk analysis of ePHI mandatory, plus security measures that cut those risks to a level you can justify. Expect to share a summary of each.

Checklist icon for HIPAA policies and retained documentation

Policies with a paper trail

45 CFR 164.316 keeps Security Rule documents on file for six years, counted from creation or from when they last applied, whichever comes later. Version history matters as much as the wording.

Audit icon for third-party assurance reports requested by US buyers

Independent assurance when asked

Larger customers may also want a SOC 2 report or an ISO/IEC 27001 certificate, issued by a CPA firm or an accredited certification body rather than a consultant. Our SOC 2 consultant page for Bangalore covers that route.

THREE REPORTING REGIMESHIPAA (you as a business associate) vs India (CERT-In directions and DPDP)
AspectHIPAA (you as a business associate)India (CERT-In directions and DPDP)
Who you notifyThe covered entity, or the upstream business associate that engaged youCERT-In for the cyber incidents listed in its 2022 directions; under DPDP, the Data Fiduciary informs the Data Protection Board and affected people
DeadlineWithout unreasonable delay, and no later than 60 calendar days after discoveryCERT-In: within 6 hours of noticing the incident. DPDP Rules: a detailed report to the Board within 72 hours once Rule 7 is in force
Reach over US patient data handled in BengaluruYes, through the BAA and the Security RuleCERT-In's FAQ says its directions apply to any entity for cyber incidents. DPDP section 17(1)(d) switches off most of Chapter II for data of people outside India processed here under a foreign contract, but keeps sections 8(1) and 8(5)
Records and logsSecurity Rule documentation kept for six yearsICT system logs kept for a rolling 180 days (CERT-In); logs and personal data kept for one year under DPDP Rule 6
Status on November 1, 2026HHS's January 2025 Security Rule proposal (90 FR 898) is still only proposed; the latest regulatory agenda shows it as long-term, aiming for a final rule in July 2027DPDP Rules notified in November 2025; most duties begin around May 13, 2027. A January 2026 proposal to shorten that to 12 months had not been notified when we checked

The practical effect: one incident at a Bengaluru vendor can start a six-hour clock in India and a contractual clock in the US on the same morning. We write a single runbook that names who files with CERT-In, who drafts the notice to the covered entity and which logs each of them will ask for.

Services

What Our HIPAA Engagement Covers for Bengaluru Business Associates

Applicability and PHI data-flow mapping

We confirm whether you are a business associate or a subcontractor, then trace every PHI path: SFTP drops, remote EHR sessions, ticket attachments, analytics extracts and backups.

Security Rule risk analysis

Administrative, physical and technical safeguards assessed against how your teams really work, with a risk register and a treatment plan your managers can own.

BAA and subcontractor review

We check that the security promises in your BAAs match what your controls can deliver and that each downstream vendor carries matching terms. Legal drafting stays with your counsel.

One runbook, three clocks

A single incident playbook for the CERT-In six-hour report, your BAA notice duties and DPDP breach steps, with log sources and NTP-synchronized timestamps identified in advance.

DPDP for your own data

Your Indian employee and customer records remain within the DPDP Act even where US patient data falls under the section 17(1)(d) exemption. Our DPDP compliance service handles notices, consent and rights requests.

Hosting and testing

If PHI workloads need a home, our HIPAA cloud hosting product comes with a signed BAA. Penetration test results can feed straight into the risk analysis.

Process

How We Deliver From Coimbatore and Chennai

Our people sit in Coimbatore and Chennai, and Bengaluru work is done remotely from there. Nobody travels to your office: the engagement runs on video calls, a shared evidence folder and written reports.

Plan your project
  1. 1

    Scoping call

    A video session with your engineering, operations and compliance leads to agree which US clients, systems and offices are in scope, and what the covered entity has asked for.

  2. 2

    Evidence request and interviews

    A structured request list, then interviews over video. Physical safeguards such as badge access and clean-desk rules are reviewed from your records, photographs and a recorded walkthrough.

  3. 3

    Risk analysis and gap register

    Findings ranked by likelihood and impact on ePHI, each with an owner, an effort estimate and the Security Rule section it maps to.

  4. 4

    Remediation with weekly written status

    Your team makes the changes; we review the evidence, rewrite policies where needed and send a short written status every week.

  5. 5

    Customer-ready pack

    Risk analysis summary, policy set, incident runbook and answers to your client's security questionnaire, ready for the covered entity's vendor review.

Working hours: Bengaluru, Coimbatore and Chennai share one clock, IST, which is UTC plus five and a half hours, so our working day is yours. When the US covered entity needs to join, a 7:30 pm IST call lands at 9:00 am in New York during US standard time and 10:00 am during daylight saving time.

Use cases

Bengaluru Teams That Usually Need a HIPAA Program

Zinnov's October 2026 review of healthcare capability centers in India notes that Bengaluru and Hyderabad lead hiring for those roles. Around them sit vendors that never thought of themselves as healthcare companies until a BAA arrived.

Healthtech SaaS with US provider customers

Scheduling, patient engagement or clinical documentation products hosted for US practices, where the BAA arrives with the first enterprise deal.

Revenue cycle and medical coding teams

Billing and claims work are named business associate functions, and the daily work runs on live claims and patient data.

IT services and cloud operations

Engineers with administrative access to a US client's EHR hosting, databases or backups handle ePHI even if they never open a chart.

Analytics and AI teams

Model training and reporting on clinical data. We check whether the data is truly de-identified or still PHI before anyone treats it as out of scope.

Capability centers of US health companies

A captive Indian entity serving its US parent still needs its HIPAA role settled on the facts before controls are designed, because that answer decides which terms and safeguards apply.

Why Xcodefix

Why Bengaluru Teams Work With Xcodefix Global

Healthcare cross icon for an established health IT practice

Healthcare is our founding practice

Xcodefix Global is the brand of Xcodefix Inc, a Delaware corporation, and its health technology work goes back to 2008, from HL7 interfaces to compliance reviews.

Expertise icon for in-house engineers who remediate HIPAA findings

Engineers who can fix what we find

More than sixty engineers and developers on our own payroll turn findings into code, configuration and test changes rather than a report on a shelf.

Response icon for same-day handling of security incidents

Same time zone, quick replies

Expect an answer to any enquiry inside one business day, and a same-day response if what you are reporting is a security incident.

Group icon for healthcare organizations on the Xcodefix client list

Bengaluru healthcare on our client list

Our clients page includes Care Bengaluru among its healthcare organizations; that relationship is shown there as held by Xcodefix India.

Start Here

Find Out What HIPAA Asks of Your Bengaluru Team

Tell us which US clients send you PHI and what they have requested. We will map your business associate duties, the Indian reporting rules that sit beside them and the shortest route to a program you can defend in a vendor review.

Prefer email? info@xcodefixglobal.com

Request a HIPAA gap review

Fields marked with an asterisk are required.

A few sentences is enough — we'll ask follow-up questions.

We use your details only to reply. See our privacy policy.
Frequently asked questions

HIPAA Consultants in Bangalore: Common Questions

Talk to the specialist who would scope the work — not a call-centre script.

Ask us directly
Is there an official HIPAA certification for companies in India?

No. HHS states that the Security Rule has no requirement to certify compliance and that it does not endorse or recognize private organizations' HIPAA certifications. A certificate also does not prevent HHS from finding a violation later. Courses can document staff training, but US buyers judge you on your BAA, your risk analysis and the safeguards you can evidence.

Do HIPAA rules apply to a company based in Bangalore?

They apply once your company handles PHI for a US covered entity or for another business associate, in any of the ways the definition lists. Being located in India does not change that definition. You take on obligations through the BAA, and 45 CFR 164.302 applies the Security Rule to business associates directly.

What is a business associate agreement?

It is the written contract a covered entity must have before sharing ePHI with a vendor. Under 45 CFR 164.314, it commits the vendor to the Security Rule, requires the same terms from its subcontractors and obliges it to report security incidents, including breaches of unsecured PHI, back to the covered entity.

How quickly must a business associate report a HIPAA breach?

45 CFR 164.410 requires notice to the covered entity without unreasonable delay and no later than 60 calendar days after discovery. That is the regulatory ceiling; your BAA can set a shorter deadline. If CERT-In's directions also cover the incident, India wants its report inside six hours.

Does India's DPDP Act apply to US patient data processed in Bengaluru?

Partly. Section 17(1)(d) disapplies most of Chapter II, plus Chapter III and section 16, where personal data of people outside India is processed in India under a contract with a person outside India. Sections 8(1) and 8(5), including reasonable security safeguards, still apply. Your Indian employee and customer data remains within the Act.

Has the HIPAA Security Rule changed in 2025 or 2026?

Not yet. HHS published a proposed rule to strengthen the Security Rule on January 6, 2025 (90 FR 898). At our November 1, 2026 check there was still no final rule; the most recent Unified Agenda places it among long-term actions, aiming at July 2027. Until then the current Security Rule governs.

Can you visit our Bengaluru office for the assessment?

No. Bengaluru work is handled remotely from Coimbatore and Chennai, and site visits are outside the scope of what we offer. Physical safeguards are reviewed through your access records, photographs and a recorded walkthrough, and interviews happen over video. Because all three cities run on IST, scheduling is easy.

How long does a HIPAA gap assessment take?

It depends on how many US clients, systems and offices are in scope and how much evidence already exists. We agree scope and a schedule on the first call instead of quoting a standard duration. Remediation time depends mostly on how quickly your engineering team can close the gaps we find.