Services
Products
Website IntelligenceLive analytics, chat & leads
Hotels & ResortsNewFront desk, bookings & compliance
Messaging for ResellersPartnerSell SMS & WhatsApp as your own
People & HRHiring to exit, one portal
Privacy TrainingNewDPDP Act training for teams
All products
About us Clients Our approach Contact
Book a free consultation +91 95003 00734
Compliance, Risk & Governance

SOC 2 Consultant in Bangalore for SaaS Companies

For Bengaluru SaaS companies whose US enterprise prospects want a SOC 2 report before they sign. We run readiness, close control gaps, build the evidence trail and prepare you for the examination, which a licensed CPA firm you engage then performs.

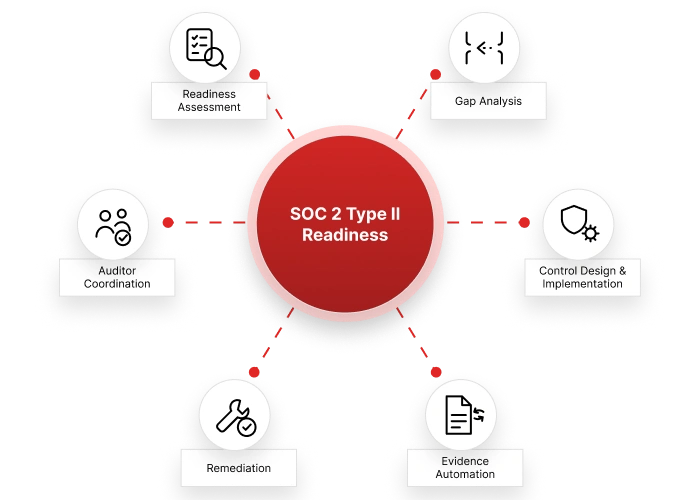
SOC 2 Type II readiness cycle showing readiness assessment, gap analysis, control design, evidence automation, remediation and auditor coordination
Standards and technologies
  • SOC 2 Type I and Type II
  • 2017 Trust Services Criteria
  • ISO/IEC 27001:2022
  • CERT-In log retention
  • DPDP Rules 2025
Challenges

Where US Deals Stall for Bengaluru SaaS Teams

The SOC 2 request rarely comes alone. It arrives with a security questionnaire, usually late in a deal, and it stalls the contract at predictable points. Each one below has a specific fix.

SOC 2 Type II control dashboard linking access control, change management, security monitoring, incident response and evidence collection

The questionnaire arrives first

A US prospect's security team sends a long questionnaire and asks for your SOC 2 report in the same email. Without one, every answer is a claim they have to take on trust, and the contract waits while procurement escalates.

Some buyers will accept a Type I report for a first contract. Others will not sign without a Type II that covers a period of operation. Knowing which buyer you face changes the whole plan.

Controls exist, evidence does not

Plenty of engineering teams already review pull requests, restrict production access and run backups. What they lack is a dated, retrievable record showing each control ran every time it should have. The CPA firm tests that record, not good intentions.

Our SOC 2 readiness assessment starts from the buyer's actual request and works backward to scope, criteria and evidence. Bengaluru companies that also process US patient data should read our HIPAA consultants in Bangalore page as well, because a BAA brings duties that SOC 2 does not cover.

Have a questionnaire on your desk?

Send it over. We will show which answers a SOC 2 report would support and which it would not.

contact us
REPORT TYPESType I vs Type II
AspectType IType II
What the CPA firm testsWhether controls are suitably designed and implemented as of one dateDesign plus operating effectiveness across a defined period
Period coveredA single point in timeAn observation window; the AICPA sets no fixed minimum
Typical window lengthNot applicableSet by each CPA firm: Schneider Downs allows 3 months for a first report and at least 6 afterward, while Wolf & Company calls 12 months common
What the report containsManagement's assertion, the system description and the auditor's opinionThe same, plus the auditor's tests of controls and their results
What a US buyer learnsYour controls exist and are sensibly designedYour controls actually ran, sample by sample, over months
Where it fitsA first enterprise deal, or a company still building its evidence habitsRenewals, and buyers whose vendor policy requires operating evidence

One workable route for an early-stage Bengaluru SaaS company is a Type I first, then a Type II whose window opens as soon as evidence collection is dependable. The window cannot usefully start before controls run consistently, so remediation comes first.

Overview

The Criteria Your Controls Are Measured Against

SOC 2 examinations use the AICPA's 2017 Trust Services Criteria, now published with revised points of focus (2022). The criteria were set by the AICPA's Assurance Services Executive Committee and span five categories. Security is required in every SOC 2 report; the other four are chosen to match what you promise customers.

Shield icon for the required SOC 2 Security category

Security (required)

Access control, change management, risk assessment, monitoring, incident response and vendor oversight. Most of your evidence will come from here.

Server icon for the SOC 2 Availability category

Availability

Include it when contracts promise uptime or recovery times. Expect capacity monitoring, backup restores and disaster recovery tests to be examined.

Encryption icon for the SOC 2 Confidentiality category

Confidentiality

Relevant when customers hand you contracts, source data or designs marked confidential. Classification, encryption and secure disposal carry the weight.

Data processing icon for the SOC 2 Processing Integrity category

Processing integrity

Suits products where accuracy is the promise, such as payroll, billing or claims calculations. Input validation and reconciliation get tested.

Personal data icon for the SOC 2 Privacy category

Privacy

Covers how personal information is collected, used, retained and disposed of. Add it when a buyer asks for it or when personal data is the product.

We use the points of focus as a design test: for each criterion in scope, does at least one of your controls clearly address its intent?

Services

What a SOC 2 Consultant Does, and What Only the CPA Firm Can Do

Under AICPA standards, SOC 2 is an attestation engagement. AICPA guidance describes SOC reports as coming from a licensed, independent CPA or a non-US equivalent, and its SOC 2 guide is written for CPAs in public practice. We are not a CPA firm and do not issue reports. Our job is everything that has to be true before the auditor starts.

Readiness assessment

Scope, system boundaries and criteria selection, followed by a control-by-control review against the TSC and a prioritized gap list.

Gap remediation

Hands-on fixes alongside your engineers: access reviews, branch protection, logging, backup restores, vendor reviews and incident drills.

Evidence collection

Evidence pulled on a schedule from your cloud, identity, CI/CD pipelines and ticketing systems, so it builds up during normal work instead of in a pre-audit scramble.

Policies people follow

Short, specific policies that match how your team works, with owners, review dates and acknowledgment records.

Auditor selection and coordination

Help shortlisting CPA firms, shaping management's system description and handling request lists during fieldwork. The firm's opinion stays its own.

Security testing

Penetration tests support your risk assessment and answer common questionnaire items. Our VAPT team can run them and retest fixes.

In practice

One Control Set for SOC 2 and ISO/IEC 27001

Bengaluru SaaS firms selling into the US and other regions are often asked for both a SOC 2 report and an ISO/IEC 27001 certificate. The two overlap heavily but are different things: SOC 2 is a CPA's attestation on your controls, while ISO/IEC 27001 certification covers an information security management system and comes from an accredited certification body.

Integration icon for controls shared between SOC 2 and ISO 27001

Shared controls

Risk assessment, access reviews, change management, logging, incident response, supplier management and backup testing can each yield one piece of evidence that serves both audits.

Documentation icon for ISO 27001 records such as the Statement of Applicability

ISO-only records

A Statement of Applicability, management review, internal audit and a defined ISMS scope have no direct SOC 2 equivalent and need their own records.

Audit icon for SOC 2 system description and operating evidence

SOC 2-only records

A system description written to the AICPA's description criteria (DC 200) and, for Type II, a full observation period of operating evidence.

Standards icon for mapping Trust Services Criteria to ISO 27001

A mapping you can trust

The AICPA publishes a spreadsheet mapping the 2017 TSC to ISO 27001, dated 2018 on its site. It predates ISO/IEC 27001:2022, so we check each line against the 2022 Annex A before relying on it.

Our ISO 27001 consulting work covers the ISMS side: scope, risk treatment, Statement of Applicability and internal audit.

In practice

The India Overlay Your Auditor Will See

A Bengaluru company's SOC 2 evidence sits inside Indian legal requirements. Building those duties into your controls means one set of evidence shows both.

Monitoring icon for CERT-In 180-day log retention

180 days of logs

CERT-In's April 2022 directions say every ICT system must keep logs for a rolling 180 days. Its FAQ accepts copies held abroad as long as CERT-In gets them within reasonable time, and names firewall, IPS, SIEM, server, VPN and application logs as examples.

Tracking icon for NTP clock synchronization

Synchronized clocks

The same directions require ICT clocks to sync with NTP servers of NIC or NPL, or sources traceable to them. Consistent timestamps also make your log evidence easier to test.

Response icon for six-hour CERT-In incident reporting

Six-hour incident reporting

Listed incidents, including data breaches and ransomware, go to CERT-In within six hours of being noticed. The FAQ lets you report what you know and add detail later. Your incident policy should name who files.

Consent management icon for DPDP Rules obligations

DPDP duties from May 2027

The DPDP Rules 2025 require a Data Fiduciary to keep logs and personal data for one year and to send the Board a detailed breach report within 72 hours. Most of these duties start around May 13, 2027.

Governance icon for mapping DPDP applicability across customer tenants

Customer data from abroad

When an Indian company processes personal data of non-residents under a contract with a foreign party, DPDP section 17(1)(d) lifts most duties but not the duty to keep reasonable security safeguards. Map which tenants fall where.

Retention settings are where these collide: 180 days for CERT-In, one year under the DPDP Rules and whatever your customer contracts specify. We set retention to the longest period that applies and document the reason.

Process

How a Remote SOC 2 Readiness Project Runs

We run Bengaluru projects from Coimbatore and Chennai without travelling. Everyone is on IST, so working sessions happen inside your normal day over video, with written updates between them.

Plan your project
  1. 1

    Buyer and scope review

    We read the customer requests you have received and agree report type, criteria, in-scope systems and the owner of each control area.

  2. 2

    Control gap assessment

    Interviews and screen-share walkthroughs of your cloud console, identity provider, repositories and ticketing. Output: a gap register ranked by audit risk and effort.

  3. 3

    Remediation sprints

    Fixes scheduled next to product work, with our engineers pairing with yours where that saves time.

  4. 4

    Evidence dry run

    We sample evidence the way an auditor would and flag anything missing, undated or inconsistent before the window opens.

  5. 5

    Observation period and fieldwork

    Monthly evidence checks during a Type II window, then help answering the CPA firm's requests during fieldwork.

No site visits: we do not travel to Bengaluru offices. If your CPA firm wants on-premises observation, that is arranged between you and the firm. For calls with a West Coast buyer or auditor, 9:30 pm IST is 8:00 am in San Francisco in winter and 9:00 am once US summer time begins.

Why Xcodefix

Why Bengaluru SaaS Teams Pick Xcodefix Global

Focus icon for readiness-only SOC 2 advice

Readiness, not reports

Because we never issue the attestation, our advice is not shaped by selling you an audit.

Project delivery icon for architect-led SOC 2 engagements

Architect-led delivery

Each project is led by an architect who reads your infrastructure as well as your policies, with a bench of more than sixty employed engineers behind them.

Healthcare icon for experience in regulated health technology

Regulated healthcare background

Since 2008 we have worked in healthcare technology, where HIPAA and SOC 2 expectations often meet in the same product.

Speed icon for one-business-day replies

Quick answers

A new enquiry is answered by the next business day at the latest, and a live security incident is picked up the day you report it.

Next Step

Get a SOC 2 Plan Your Sales Team Can Quote

Share the security questionnaire or SOC 2 request you have received. We will recommend Type I or Type II, the criteria to include and the evidence gaps to close first.

Prefer email? info@xcodefixglobal.com

Start SOC 2 readiness

Fields marked with an asterisk are required.

A few sentences is enough — we'll ask follow-up questions.

We use your details only to reply. See our privacy policy.
Frequently asked questions

SOC 2 Consultant in Bangalore: Questions We Hear

Talk to the specialist who would scope the work — not a call-centre script.

Ask us directly
Which firms may sign a SOC 2 report for an Indian company?

SOC 2 is an AICPA attestation engagement. AICPA guidance says the reports come from a licensed, independent CPA or a non-US equivalent, and its SOC 2 guide is addressed to CPAs in public practice. Consultants, compliance software and training providers cannot issue one, so ask any provider which licensed firm will sign the opinion.

What is the difference between SOC 2 Type I and Type II?

Type I reports whether your controls are suitably designed as of a single date. Type II also tests whether they operated effectively throughout a defined period, and the report includes the auditor's tests and results. Some US buyers accept a Type I for a first deal while others insist on Type II from the start, so ask before you plan.

How many months should our first Type II window cover?

The AICPA does not set a minimum, so CPA firms set their own expectations. Schneider Downs, for example, allows three months for a first report and at least six months afterward, preferring twelve, while Wolf & Company describes twelve months as common. Agree the window with your auditor before evidence collection starts.

Can a SOC 2 consultant also be our auditor?

Not for the same work. AICPA guidance describes the issuer as an independent CPA, and a firm that designed and built your controls is poorly placed to attest to them. We do readiness only. You engage the CPA firm directly, and we coordinate with it during fieldwork.

Does a SOC 2 report replace ISO 27001 certification?

No. They share many controls, but ISO/IEC 27001 certifies an information security management system through an accredited certification body, while SOC 2 is an attestation report. Running both from one control set avoids duplicate work, although ISO-specific records such as the Statement of Applicability and management review still need their own evidence.

Do CERT-In rules affect our SOC 2 logging?

Yes. The 2022 CERT-In directions call for 180 days of logs from every ICT system, clocks tied to NIC or NPL time sources, and a six-hour deadline for reporting listed incidents. Building these into your logging and incident controls means the evidence you give your auditor also shows how you meet Indian requirements.

Which Trust Services Criteria should a SaaS company include?

Security is mandatory. Add Availability if contracts promise uptime, Confidentiality if customers share confidential material, Processing Integrity if accurate calculations are the product, and Privacy when a buyer asks or personal data is central. Including criteria nobody asked for widens audit scope and cost without helping sales.

Do you work on-site in Bangalore?

No. Our engineers stay in Coimbatore and Chennai and work with Bengaluru clients remotely: same time zone, video working sessions and a written status note each week. Any on-premises observation your CPA firm needs is arranged directly between you and the firm.