Services
Products
Website IntelligenceLive analytics, chat & leads
Hotels & ResortsNewFront desk, bookings & compliance
Messaging for ResellersPartnerSell SMS & WhatsApp as your own
People & HRHiring to exit, one portal
Privacy TrainingNewDPDP Act training for teams
All products
About us Clients Our approach Contact
Book a free consultation +91 95003 00734
Telecom & Messaging

HIPAA Compliant SMS API Design for Patient Messaging

For US practices, health systems and digital health teams that need to text patients without exposing PHI. We build the messaging layer on a carrier API that signs a Business Associate Agreement: what each text may say, what stays behind a secure link, and the consent, logging and carrier registration around it.

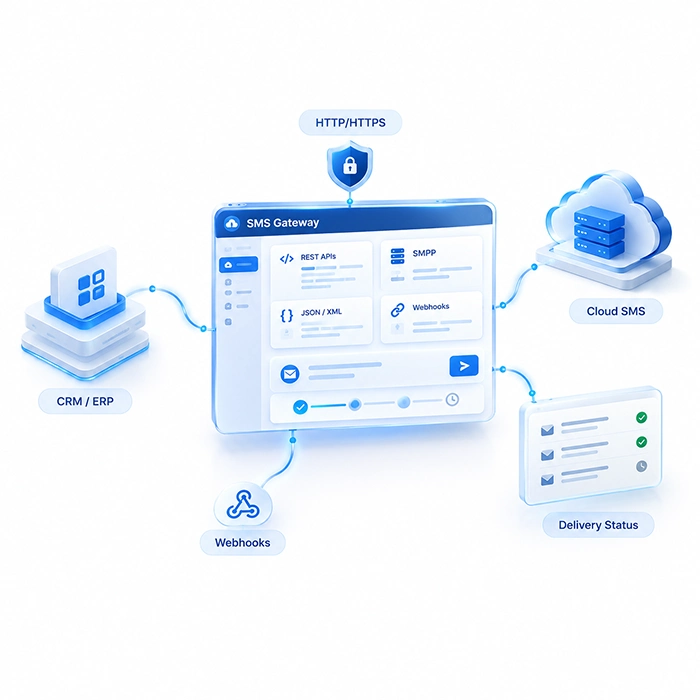
SMS API gateway connected over HTTPS to a CRM, webhooks, delivery status and a cloud SMS service, the integration layer behind HIPAA-safe patient texts
Standards and technologies
  • HIPAA Security Rule
  • Business Associate Agreement
  • TCPA Consent
  • 10DLC Registration
  • Toll-Free Verification
  • Secure Links
Challenges

Why Patient Texting Fails a HIPAA Review

The carrier API is rarely the weak point. Problems hide in templates, vendor contracts and missing records.

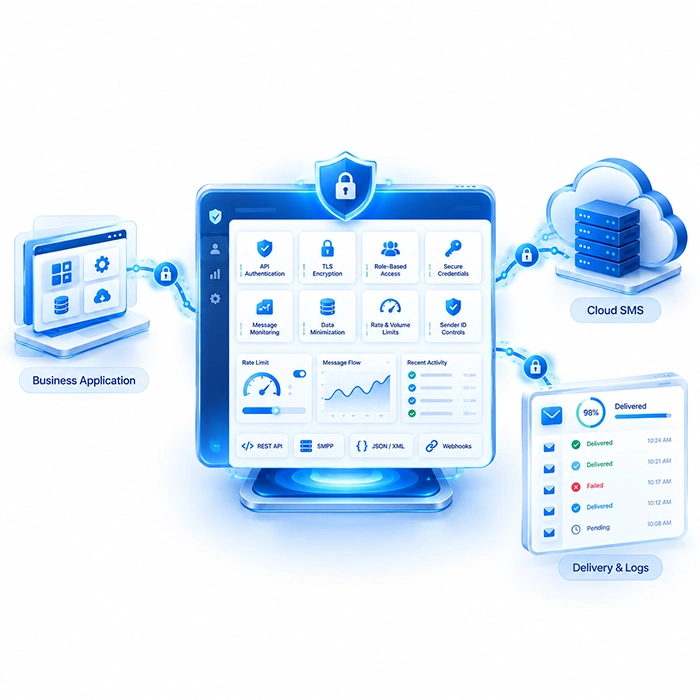
Business application sending through a secured messaging gateway to a cloud SMS provider, with delivery logs flowing back, the path a patient text travels

What a Single Text Can Expose

Once a text is sent, it sits in places you do not manage:

  • Carrier networks: CISA's mobile communications guidance states that SMS messages are not encrypted and can be read by anyone with access to a provider's network
  • Lock-screen previews on a phone shared with family
  • A number that has since been reassigned to someone else
  • Message logs kept by every platform between your EHR and the handset

Gaps We Find in Existing Builds

  • An SMS vendor with no BAA, or a BAA that excludes the product actually in use
  • Diagnoses, drug names or test types typed into reminder templates
  • No record of when or how the patient agreed to receive texts
  • STOP replies that never reach the scheduling system
  • Sending numbers that were never registered with the carriers

Our own Messaging Hub and bulk SMS gateway are built for high-volume sending and India's DLT rules, and neither page makes a HIPAA claim. For US patient texting we build on a carrier API whose BAA covers the exact product you use, then write the templates, code and controls on top.

Texting patients already?

Send us one template and your vendor's BAA. We will tell you what an investigator would question first.

contact us
Overview

What HHS and OCR Have Said About Texting Patients

No HIPAA rule is written specifically for SMS. The position comes from the Privacy Rule's safeguards standard, OCR guidance on email, and public statements by OCR.

Reasonable Safeguards, Not a Ban

HHS's FAQ on patient email says providers may communicate electronically if they apply reasonable safeguards under 45 CFR 164.530(c), such as limiting the amount or type of information in an unencrypted message. Any ePHI transmission must still satisfy the Security Rule.

Patient Preference After a Warning

In the 2013 Omnibus Rule preamble, HHS said covered entities may send unencrypted email to individuals who were told of the risk and still prefer it. Its right of access guidance follows the same logic: if a warned patient asks for an unsecure channel, you are not liable for interception in transit.

OCR on Texts Specifically

At HIMSS in March 2018, then-OCR Director Roger Severino was asked why OCR had email guidance but none for texting. He said he did not see a difference. That was a conference remark rather than formal guidance, so we design to the written rules first.

None of this exempts your own systems: the service that composes, queues and logs messages holds ePHI and needs access controls, audit controls (164.312(b)) and transmission security (164.312(e)).

MESSAGE DESIGNPHI in the SMS body vs Secure link to an authenticated page
AspectPHI in the SMS bodySecure link to an authenticated page
Shown on a lock screenVisit type, provider, sometimes resultsPractice name and a prompt to sign in
Carried over the networkReadable health detailsA short, expiring link token
Wrong or reassigned numberHealth details reach a strangerA stranger sees a sign-in step they cannot pass
Held in vendor logsFull clinical wordingThe notice text and token only
Evidence for an investigatorNo record of who read whatAccess log showing who opened the content and when
Effort for the patientNoneOne check, such as date of birth plus a code

The minimum-necessary standard at 164.502(b) does not apply to disclosures made to the patient, but it does apply to what vendors receive, and a secure link keeps clinical detail out of their logs. A reminder with only a date, time and practice name exposes little, and your risk analysis can record that choice. Results and care-plan messages go behind the link.

Who it suits

Which SMS Providers Sign a BAA, and for What

A BAA is only as useful as its product scope. The terms below come from vendor pages checked on November 1, 2026; they change, so we confirm scope in writing before any build.

SMS icon for Twilio's HIPAA-eligible messaging products

Twilio

Twilio signs a Business Associate Addendum for products on its HIPAA-eligible list, and only for accounts on its Security or Enterprise Edition. Programmable SMS became eligible on March 20, 2020 and MMS on September 30, 2021. Products outside the list must not carry PHI.

Messaging icon for Bandwidth's BAA-covered messaging API

Bandwidth

Bandwidth began offering a BAA for its messaging and voice APIs on March 20, 2023. Its help center says the BAA is meant for healthcare customers whose use case may include PHI in the content of US messages or calls, limited to its HIPAA-eligible products.

Cloud icon for AWS End User Messaging under the AWS BAA

AWS End User Messaging

AWS lists Amazon Pinpoint and End User Messaging as HIPAA eligible, excluding voice message capabilities and the WhatsApp channel (list updated October 15, 2026). Customers accept the AWS BAA through AWS Artifact in the console.

Why the vendor needs a BAA: HHS limits the conduit exception to transmission-only services with transient storage. A platform that keeps message bodies, logs or contact lists maintains PHI, which makes it a business associate. On March 5, 2026, OCR announced a settlement with MMG Fusion, a business associate whose software communicates directly with patients, after a breach affecting about 15 million people and a failure to conduct an accurate risk analysis.

In practice

Consent Rules That Sit Beside HIPAA

HIPAA governs what a text may contain. The TCPA governs whether you may send it. The FCC rules at 47 CFR 64.1200 treat a text message as a call.

Consent management icon for recording patient texting consent

Prior Express Consent

Texts sent with autodialing equipment to a mobile number need the patient's prior express consent, and promotional texts need prior express written consent. We store the source, wording, timestamp and number behind every consent.

Healthcare icon for the FCC healthcare messaging exemption

The Healthcare Exemption

Section 64.1200(a)(9)(iv) exempts provider texts that cost the patient nothing and cover appointment reminders, wellness checkups, pre-registration and pre-operative instructions, lab results, post-discharge follow-up, prescription notices or home healthcare instructions. Each must go only to the number the patient gave, name the provider, stay within 160 characters, offer STOP, avoid billing and marketing content, comply with HIPAA, and keep to one a day and three a week.

Message icon for opt-out and revocation handling

Revocation

Under 64.1200(a)(10), patients may revoke consent by any reasonable means. Replies such as stop, quit, end, revoke, opt out, cancel or unsubscribe count automatically, and revocations must be honored within ten business days. Opt-outs from exempt healthcare texts must be honored immediately.

Services

What We Build Around the Carrier API

Template Library With PHI Checks

Approved templates for each message type, plus a pre-send check that blocks free text containing diagnosis terms, drug names or record numbers.

Secure-Link Message Center

Single-use, short-lived tokens with no PHI in the URL, leading to identity verification and an authenticated page built as described in HIPAA compliant website development. It can run on our HIPAA Cloud Hosting, which comes with a signed BAA.

EHR and Scheduling Triggers

Reminders fired by scheduling events from the EHR through the HL7 and FHIR interfaces we build, so a cancellation also cancels the next text.

Consent and Opt-Out Ledger

A single record of consent source, preferred channel and revocations, kept in step with the provider's opt-out list and your EHR.

Patient Verification Codes

Code generation, expiry and rate limiting modeled on our 2FA/OTP API, used to confirm the patient before the secure page opens.

Delivery and Access Logs

Delivery receipts, failures, link opens and page views written to an append-only log, kept for the period your policy sets.

Process

How We Take a Patient Messaging Program Live

Plan your project
  1. 1

    Classify Every Message

    We list each message you send or plan to send, mark which ones carry PHI, and choose plain SMS, a secure link or no text at all.

  2. 2

    Choose the Provider and Confirm the BAA

    We match your volumes and channels to a provider whose BAA names the product you will use, and record that scope in your vendor inventory.

  3. 3

    Write Templates and Consent Wording

    Templates, opt-in language, HELP and STOP replies, and the warning shown to patients who ask for details by plain text.

  4. 4

    Register With the Carriers

    Brand and campaign registration for 10DLC numbers, or toll-free verification, with sample messages and an opt-in description that match what you will really send.

  5. 5

    Build and Test the Edge Cases

    EHR integration, the secure page and the logs, tested against wrong numbers, expired links, opt-outs and failed deliveries.

  6. 6

    Hand Over the Evidence

    Data-flow diagram, BAA list, template register and log samples go to your compliance lead as input for the next HIPAA risk analysis.

Carrier registration realities: Twilio blocks US-bound messages from any 10DLC number not tied to an approved campaign, and since January 31, 2024 it has blocked unverified toll-free traffic. Neither process reviews HIPAA safeguards; carriers check identity, consent and content. Approval times sit with the carriers, so we start registration early.

Why Xcodefix

Why Xcodefix for HIPAA-Safe Patient Messaging

Message icon representing hands-on messaging engineering

Messaging Engineers First

We built and run our own messaging platform, so routing, delivery receipts and failover are familiar work. We apply that experience on a BAA-covered US provider.

Compliance icon for HIPAA review of messaging flows

Compliance in the Same Team

Our HIPAA compliance consultants review the templates and data flows our engineers build, so nothing falls into a handover gap.

Expertise icon for architect-led delivery

Architect-Led Delivery

A solution architect owns the design from message classification to go-live, supported by 60+ in-house engineers in Coimbatore and Chennai and a healthcare practice that dates to our founding in 2008.

Response icon for reply times

Quick Answers

We reply to enquiries within one business day; a suspected breach or active attack gets a response the same day.

Get Started

Text Patients Without Putting PHI on the Lock Screen

Share your current templates, provider and consent flow. We will show which messages are fine as plain SMS, which need a secure link, and what your BAA really covers.

Prefer email? info@xcodefixglobal.com

Request a Messaging Review

Fields marked with an asterisk are required.

A few sentences is enough — we'll ask follow-up questions.

We use your details only to reply. See our privacy policy.
Frequently asked questions

HIPAA Compliant SMS: Common Questions

Talk to the specialist who would scope the work — not a call-centre script.

Ask us directly
Is there such a thing as a HIPAA compliant SMS API?

No API is HIPAA compliant by itself. A provider can sign a BAA and secure its platform, but compliance depends on what you put in messages, who can read the logs, how consent is recorded and whether your risk analysis covers the flow. Twilio, Bandwidth and AWS End User Messaging offer BAA coverage for certain products, each with conditions.

Can doctors text patients under HIPAA?

Yes, with reasonable safeguards. HHS guidance permits electronic communication with patients when providers limit what they send and protect their own systems. A patient who has been warned that texting is not secure may still choose it. Keep clinical details behind a secure link where you can, and honor any request for a different channel.

Do we need a BAA with our SMS provider?

Yes, if the provider stores or processes PHI for you. HHS treats a vendor that keeps message content, logs or contact lists as a business associate, not a conduit. Check that the BAA names the specific product, such as programmable SMS, and that your account tier qualifies, because some vendors sign only for higher plans.

Is SMS encrypted?

Standard SMS is not end-to-end encrypted. CISA's mobile communications guidance warns that SMS messages can be read by anyone with access to a telecom provider's network. Your server's API call to the provider runs over TLS, but the leg to the handset lacks that protection. That is why we keep clinical content out of the message body.

What can a HIPAA compliant text message say?

Limit it to what a stranger could see without harm: the practice name, a date and time, and an instruction such as signing in to read a message. Leave out diagnoses, test names, medications and the reason for the visit. Results and care instructions belong on an authenticated page reached through a short-lived link.

Do healthcare organizations need 10DLC registration?

Yes, if you send application-to-person texts from standard 10-digit US numbers. Brand and campaign registration is required, and Twilio blocks messages from 10DLC numbers not tied to an approved campaign. Toll-free numbers need toll-free verification instead. Both processes check consent and content; neither reviews your HIPAA safeguards.

Which HIPAA compliant SMS providers should we consider?

Start with providers that publish BAA terms for messaging: Twilio for HIPAA-eligible products on its Security or Enterprise Edition, Bandwidth for its messaging API, and AWS End User Messaging under the AWS BAA. Compare BAA scope, log retention controls, delivery reporting and fit with your volumes. We help shortlist and then integrate whichever fits.

Does TCPA consent apply to appointment reminders?

Yes. The FCC treats texts as calls. Reminders can fall under the healthcare exemption at 47 CFR 64.1200(a)(9)(iv) if they are free to the patient, go only to the number the patient provided, stay concise, offer STOP and keep to one a day and three a week. Outside those limits, rely on documented prior express consent.