Services
Products
Website IntelligenceLive analytics, chat & leads
Hotels & ResortsNewFront desk, bookings & compliance
Messaging for ResellersPartnerSell SMS & WhatsApp as your own
People & HRHiring to exit, one portal
Privacy TrainingNewDPDP Act training for teams
All products
About us Clients Our approach Contact
Book a free consultation +91 95003 00734
Healthcare IT & Interoperability

Healthcare IT Company in Chennai for Hospitals and Labs

For Chennai hospitals, diagnostic labs and imaging centers that already own their software and need it connected, secured, hosted and supported. Our team in Chennai handles HIS, LIS and PACS interfaces, penetration testing, incident response, cloud migration and day-to-day operations, with CERT-In and NABH expectations built in.

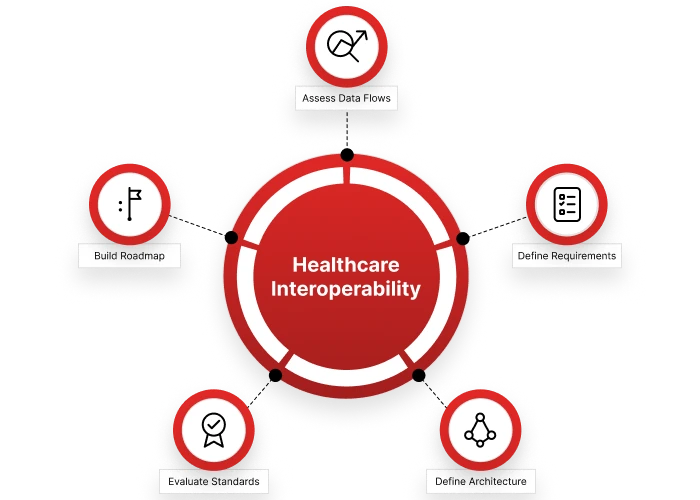
Healthcare interoperability planning cycle covering data flows, requirements, standards, architecture and roadmap for hospital systems
Standards and technologies
  • HIS, LIS and PACS
  • HL7 v2 and DICOM
  • VAPT
  • CERT-In Directions 2022
  • NABH digital health
  • DPDP Act 2023
Challenges

Where Hospital IT Breaks Down

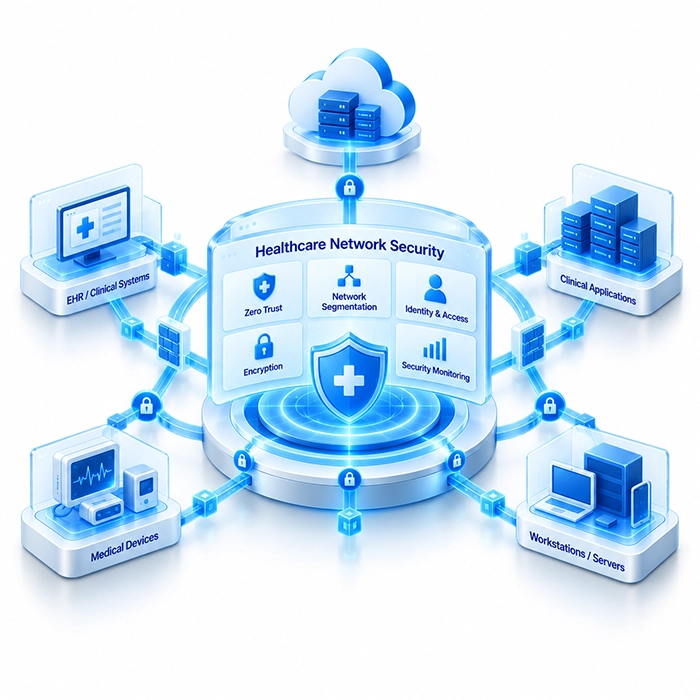
Hospital network security architecture linking EHR, clinical applications, medical devices and servers through segmented, encrypted connections

Systems bought one at a time

The HIS came from one vendor, the LIS from another and the PACS from a third. Results get re-typed, patient demographics drift apart between systems, and when a report goes missing nobody can say which interface dropped it.

Each vendor supports its own product and points at the others once data stops flowing.

Security without a clear owner

CERT-In's India Ransomware Report for 2024 names LockBit, RansomHub and KillSec as the dominant groups, describes attackers encrypting whole fleets of virtual machines through VMware ESXi hypervisors, and traces continued exposure to gaps in access control, patch management and monitoring. Those are precisely the gaps a stretched hospital IT team finds hardest to close.

We treat both problems as one estate: an interface map and a security map drawn from the same inventory. The strategy layer sits with our healthcare interoperability consulting; active threats go to our incident response service.

Systems down right now?

Mark your message urgent. We start on security incidents the day they are reported.

contact us
Overview

Connecting HIS, LIS, PACS and Devices

Interoperability inside a hospital is mostly plumbing: dependable message routes, shared identifiers and agreed codes. The September 2025 second edition of NABH's hospital digital health standards lists SNOMED CT or WHO ICD terminology, LOINC-tagged lab results and DICOM compliance among their information management objectives.

Integration icon for HIS to LIS order and result interfaces

HIS to LIS

Orders out and results back as HL7 v2 messages through Mirth Connect, with acknowledgments, retries and an alert when a result fails to reach the patient's record.

EMR integration icon for HIS to PACS connections

HIS to PACS and RIS

Patient and order context passed to imaging and report status returned, so radiology never re-registers a patient the HIS already knows.

Technology icon for lab analyzers and connected medical devices

Analyzers and connected devices

Lab analyzers usually reach the HIS through the LIS, and we work at that interface. Connected devices are inventoried so they can be segmented and monitored.

Patient card icon for patient identity matching

One patient, one identifier

Matching rules and a reconciliation queue for duplicate registrations, so a result never attaches to the wrong person.

Interface work runs through our Mirth Connect development and support practice. If you are commissioning new clinical software rather than connecting existing products, see healthcare software development in Chennai.

Services

Healthcare IT Services We Run for Chennai Providers

VAPT for clinical and public systems

Patient portals, mobile apps, APIs, internal networks and cloud accounts tested manually and with tools, and checked again after you patch.

Incident response and forensics

Containment, evidence preservation, root-cause analysis and recovery planning when ransomware or a data leak hits.

Cloud migration

HIS servers, imaging archives and backups moved to AWS through a planned cloud migration: landing zone, phased waves and rollback plans, with logging set for CERT-In retention.

Managed hosting and patching

Monitoring, operating system and application patching, verified daily backups and hardening for the servers and sites you hand over to us.

Interface engine support

Monitoring and fixes for existing HL7 channels, plus documentation for the channels nobody on staff remembers building.

Compliance evidence

Evidence packs for NABH digital health assessments and DPDP readiness, drawn from the controls we operate for you.

Testing follows our VAPT methodology, and hosting follows our managed web hosting operating model.

In practice

What CERT-In and NABH Expect From Hospital IT

Two documents set much of the baseline for a private hospital's IT in India: CERT-In's directions of April 28, 2022, and NABH's digital health standards. The DPDP Rules add further duties from May 2027.

Response icon for six-hour cyber incident reporting

Report within six hours

Ransomware, data breaches, data leaks and unauthorized access to IT systems are among the incidents CERT-In wants reported no later than six hours after you notice them. Name a point of contact in advance.

Monitoring icon for 180-day log retention

Keep 180 days of logs

Every server, firewall and application logging to secure storage that holds 180 days at a time, with clocks set from NIC or NPL time servers.

Encryption icon for data encrypted at rest and in transit

Encrypt and audit

NABH's Digital Infrastructure chapter expects encryption at rest, including cloud backups, and in transit; antivirus and firewalls on endpoints; and audit trails for core healthcare applications.

Backup icon for network, power and downtime continuity

Keep working when systems fail

The same standards look for redundant network links, power backup and offline capture of patient data during downtime that syncs back to the HIS when it recovers.

Personal data icon for DPDP Rules obligations

Prepare for DPDP

From around May 13, 2027, Rule 6 adds one-year retention of logs and personal data, and Rule 7 a detailed breach report to the Data Protection Board within 72 hours.

NABH lets hospitals apply for digital health recognition at Silver, Gold or Platinum maturity levels. We map each technical objective to an owner and a piece of evidence, so the assessment becomes a records exercise. The state's 2018 rules for clinical establishments in Tamil Nadu add that every record must be open to inspection by the competent authority, which is far easier when records sit in systems with reliable search and access logs.

Process

The First Hours of a Hospital Ransomware Incident

This is how we work when a Chennai hospital calls during an attack. Our engineers are in the same city, and we pick up security incidents on the day you call.

Plan your project
  1. 1

    Contain without destroying evidence

    Isolate affected hosts and hypervisors from the network, but leave them as untouched as possible so memory and logs survive for analysis.

  2. 2

    File the CERT-In report

    Get the first report to CERT-In inside the six-hour window with the facts available; its FAQ lets the rest follow. We draft it with your point of contact.

  3. 3

    Switch to downtime procedures

    Registration, orders and notes move to the offline procedure you prepared, so care continues while systems are down.

  4. 4

    Scope and eradicate

    A timeline built from synchronized logs, the entry point identified, persistence removed and credentials reset before anything is restored.

  5. 5

    Restore and review

    Restore from backups confirmed clean, reconcile downtime records into the HIS, and close with a written report and a list of fixes.

Before any incident: each of these steps depends on preparation. Backups nobody has test-restored, logs that rotate after a week and an unnamed CERT-In contact are the gaps we close first.

Why Xcodefix

Why Chennai Providers Work With Xcodefix Global

Team icon for the Chennai healthcare IT delivery team

A Chennai delivery team

Our engineers are in Chennai and Coimbatore. Xcodefix Global, the brand they work under, belongs to Delaware's Xcodefix Inc and has done health technology work since 2008.

Shield icon for combined integration and security expertise

Integration and security together

The people who maintain your interfaces also understand how attackers move through them, which shortens incident scoping.

Customers icon for Chennai healthcare clients

Known in Chennai healthcare

Our clients page shows Care Chennai in its healthcare group, with the relationship held by Xcodefix India.

Support icon for fast replies to hospital IT enquiries

Answers within a day

Routine questions are answered within a business day; incidents are handled the day you raise them.

Talk to Us

Get a Clear Picture of Your Hospital's IT Risk

Send us your system list or your latest audit findings. We will come back with the interfaces most likely to fail, the security gaps most likely to be exploited and the order in which to fix them.

Prefer email? info@xcodefixglobal.com

Book a healthcare IT review

Fields marked with an asterisk are required.

A few sentences is enough — we'll ask follow-up questions.

We use your details only to reply. See our privacy policy.
Frequently asked questions

Healthcare IT Company in Chennai: Questions Answered

Talk to the specialist who would scope the work — not a call-centre script.

Ask us directly
What does a healthcare IT company do for a hospital?

It keeps the hospital's technology connected, secure and running: interfaces between HIS, LIS and PACS, network and application security, backups, cloud or data center hosting, support and compliance evidence. Building new software is a separate service; this page covers running and protecting the systems you already have.

Do Chennai hospitals have to report cyber incidents to CERT-In?

CERT-In's directions of April 28, 2022 cover service providers, data centers, body corporates and government organizations, and require listed incidents to be reported within six hours of noticing them. CERT-In's FAQ defines body corporate broadly, including firms and sole proprietorships in commercial or professional activity, which takes in most private hospitals.

How long must hospital IT logs be kept in India?

Keep at least 180 days, on a rolling basis, for every ICT system: that is CERT-In's floor, and the logs must be handed over when CERT-In asks. Holding copies abroad is acceptable under its FAQ provided they can be produced promptly. From around May 2027, the DPDP Rules add one-year retention of logs and personal data for breach investigation.

What does NABH digital health accreditation check in IT?

NABH's hospital digital health standards span infrastructure, operations and information management. IT-heavy objectives include encryption at rest and in transit, endpoint antivirus and firewalls, audit trails for core applications, network and power redundancy, offline capture during downtime, and use of SNOMED CT or ICD, LOINC and DICOM.

Can you connect our LIS and PACS to the HIS?

In most cases. We list what each product can send and receive, build the routes in Mirth Connect or another engine you already license, and put monitoring on every channel so a rejected order or result raises an alert instead of vanishing quietly.

Do you provide on-site IT support in Chennai?

Our Chennai and Coimbatore teams deliver these services mainly through remote access, monitoring and scheduled working sessions with your hospital's own IT staff. We do not repair desktops or handle hardware; we coordinate with your in-house staff or hardware vendor whenever physical work is needed.

Is this page about healthcare IT jobs in Chennai?

No. It describes the services we provide to hospitals, diagnostic labs and imaging centers. Some visitors arrive looking for healthcare IT roles; if you are an engineer interested in our Chennai or Coimbatore teams, write to info@xcodefixglobal.com. We do not advertise vacancies on this page.

How is healthcare IT different from your healthcare software service?

Healthcare IT keeps existing systems connected, secure and hosted. Our healthcare software development service builds new modules, apps and integrations. Many hospitals need both, in that order: stabilize and protect what runs today, then extend or replace it. Each has its own page so you can see which one fits.