Services
Products
Website IntelligenceLive analytics, chat & leads
Hotels & ResortsNewFront desk, bookings & compliance
Messaging for ResellersPartnerSell SMS & WhatsApp as your own
People & HRHiring to exit, one portal
Privacy TrainingNewDPDP Act training for teams
All products
About us Clients Our approach Contact
Book a free consultation +91 95003 00734
Web, Digital & Domains

HIPAA Compliant Chatbot for Healthcare Websites

For providers and digital health companies adding an AI assistant to a website or portal. We decide with you when the bot may handle PHI, put a BAA behind every vendor that sees a conversation, and build the sign-in, transcript controls, clinical guardrails and human handoff that make it safe to run.

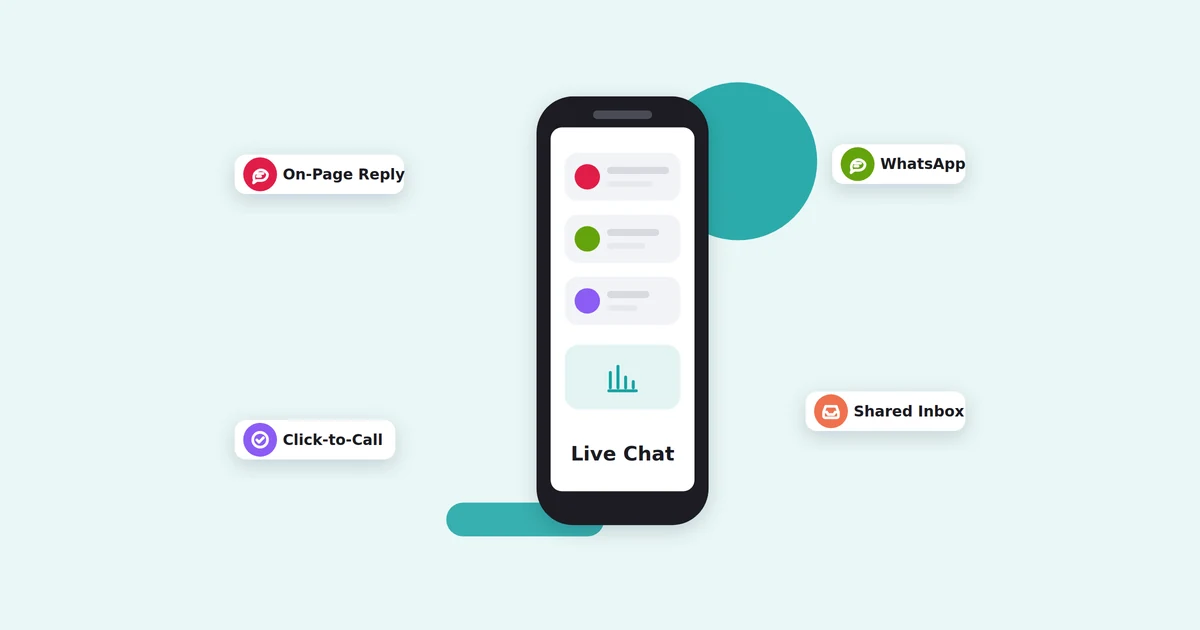
Website chat on a phone with on-page replies, click-to-call, WhatsApp and a shared inbox, the conversation channels a healthcare chatbot connects to
Standards and technologies
  • Business Associate Agreement
  • Azure OpenAI
  • Amazon Bedrock
  • OpenAI API
  • OCR Tracking Bulletin
  • Human Handoff
Challenges

When a Website Chatbot Becomes a HIPAA System

A chatbot that answers parking questions is a content tool. Once it accepts a name with a symptom, an appointment request or a date of birth on a provider's site, it is handling PHI.

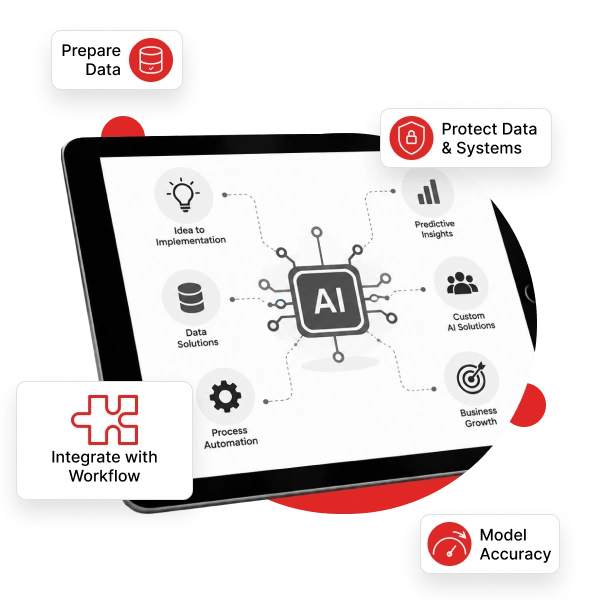
Tablet showing an AI system connected to data preparation, data protection, workflow integration and model accuracy, the controls a HIPAA compliant chatbot relies on

Signs Your Bot Handles PHI

  • It asks for or accepts names, dates of birth, phone numbers or member IDs
  • Visitors describe symptoms, medications or conditions
  • It books, changes or cancels appointments
  • It runs inside the patient portal or reads records
  • Staff store and review its transcripts

Where Projects Go Wrong

  • A chat vendor or AI provider with no BAA, or one that excludes the features in use
  • Transcripts copied into analytics, CRM or ticketing tools
  • Chat widgets that share page and session data with ad platforms
  • A bot that answers clinical questions without limits
  • No route to a person when the bot is out of its depth

Our live chat software is built for enquiries and sales conversations and is joined to visitor analytics. Its page makes no HIPAA claim, so we do not deploy it as a PHI channel. Patient-facing assistants come from our AI and machine learning practice, built on BAA-covered infrastructure.

Already running a chatbot?

Send us the vendor names and a sample transcript export. We will show you where PHI ends up.

contact us
SCOPE DECISIONGeneral FAQ bot vs PHI-capable assistant
AspectGeneral FAQ botPHI-capable assistant
Allowed inputsHours, directions, services, insurance plans acceptedSymptoms, appointments, records, bills
BAA chainNot needed if no PHI is collectedChat platform, AI provider, storage and hosting
IdentityAnonymous, with a visible warning against sharing health informationVerified sign-in before PHI is shown or accepted
TranscriptsShort retention, no identifiersEncrypted storage, access logs, defined retention
TrackingSite analytics that never see chat contentNo third-party tags in the chat frame
EscalationPhone number and contact formHandoff to staff inside the same thread

Launching with the left column and adding PHI capability once the BAA chain and sign-in exist is a sound path. The real mistake is a left-column bot that quietly collects right-column data.

Overview

AI Providers and BAAs: The Conditions That Matter

Terms checked on November 1, 2026. Each comes with conditions that change, so we confirm coverage in writing for your account before any PHI is sent.

Generative AI icon for OpenAI API models

OpenAI

OpenAI reviews API BAA requests case by case through baa@openai.com and says most API services are covered, with listed exceptions. For ChatGPT, sales-managed Enterprise and Edu accounts are eligible; ChatGPT Business is not.

Cloud services icon for Azure OpenAI

Azure OpenAI in Microsoft Foundry

Microsoft's BAA needs no separate signature: it is part of the Product Terms and the Data Protection Addendum that apply to any customer that is a covered entity or business associate. Prompts are not used to train models, but default abuse monitoring can store flagged prompts for human review unless you are approved for modified monitoring.

AWS icon for Amazon Bedrock

Amazon Bedrock

AWS lists Amazon Bedrock as a HIPAA eligible service (list updated October 15, 2026). The AWS BAA is accepted through AWS Artifact, and only eligible services may store or process PHI.

Machine learning icon for Google's agent platform

Google Gemini Enterprise Agent Platform

Google's former Vertex AI pages now redirect to Gemini Enterprise Agent Platform, and its Cloud BAA lists Generative AI on Agent Platform. Google's HIPAA guidance says not to place PHI in conversational agent definitions such as intents and training phrases.

A BAA with the model provider is only one link. The chat widget, vector database, logging service and hosting all see conversation data, and each needs coverage too.

In practice

Four Design Rules for Patient-Facing Chat

Data storage icon for encrypted chat transcripts

Treat Transcripts as PHI

Store them encrypted under a BAA, record each access in line with the 164.312(b) audit controls, and set retention deliberately. If staff use transcripts to make decisions about patients, they can fall within the designated record set and the patient's right of access.

Security icon for patient sign-in before PHI

Authenticate Before PHI

Public chat stays general. Anything personal waits until the patient signs in through the portal or a verified code, and idle sessions end, an addressable control under 164.312(a)(2)(iii).

Tracking icon for keeping pixels out of chat

Keep Trackers Out of the Chat

OCR's tracking bulletin, still in force apart from the IP-address-plus-public-page portion vacated in 2024, says symptoms typed into a tool on an unauthenticated page can be identifiable health information. We load chat in its own frame with no third-party tags and send nothing from it to analytics.

Bot icon for chatbot guardrails and handoff

Guardrails and Human Handoff

The bot answers from approved content, declines diagnosis and dosing questions, and routes urgent phrases to emergency instructions and staff. In California, Health and Safety Code 1339.75 requires health facilities, clinics and physician offices using generative AI for clinical patient messages to disclose it throughout a chat and explain how to reach a human, unless a licensed provider reviews the message.

Services

What We Build

Scope and Data-Flow Design

Which intents the bot handles, what data each one needs, and which vendors see it.

Retrieval on Approved Content

Answers grounded in your reviewed pages, policies and FAQs, so the model is not improvising medical content.

Portal and EHR Connection

Authenticated appointment and record lookups over FHIR APIs, drawing on the interface skills of our HL7 and FHIR integration practice.

Staff Handoff Inbox

Escalated conversations arrive with context in a BAA-covered tool your team already watches.

BAA-Covered Hosting

The assistant, vector store and logs run on our HIPAA Cloud Hosting or in your own BAA-covered cloud account.

Testing and Monitoring

Adversarial prompts for data leakage and unsafe advice before launch, plus ongoing answer review. The surrounding infrastructure goes through HIPAA penetration testing.

Process

How a HIPAA Chatbot Project Runs

Plan your project
  1. 1

    Define the Bot's Job

    List the questions it will answer, the actions it may take and the cases it must hand off.

  2. 2

    Confirm the BAA Chain

    Chat layer, model provider, storage and hosting, each confirmed in writing for the features you will use.

  3. 3

    Prepare Approved Content

    Clinical and operations staff review the sources the bot will answer from.

  4. 4

    Build Sign-In, Guardrails and Handoff

    Identity checks, refusal rules, emergency routing and the staff inbox.

  5. 5

    Test With Real Questions

    Patient-style questions, adversarial prompts and edge cases, reviewed by your clinicians before launch.

  6. 6

    Launch, Monitor, Improve

    Transcript sampling under access controls, answer corrections and periodic retesting.

Project realities: Vendor BAA confirmation and clinical content review often take longer than the build itself. We plan around both from the first week.

Why Xcodefix

Why Xcodefix for a HIPAA Compliant Chatbot

AI automation icon for combined AI and healthcare engineering

AI and Healthcare in One Team

The engineers building the assistant work with our interface and compliance specialists, so model choice, data flow and HIPAA review happen together.

Practical icon for honest product recommendations

Straight Product Advice

When one of our own products is the wrong fit for PHI, we say so and build on infrastructure that is covered.

Expertise icon for engineering depth

Depth of Team

60+ in-house engineers working from Coimbatore and Chennai under an architect-led model.

Get Started

Put a Safe Assistant on Your Website

Tell us what you want the bot to do and which vendors you are considering. We will map the data flow, the BAAs you need and the guardrails to build first.

Prefer email? info@xcodefixglobal.com

Request a Chatbot Assessment

Fields marked with an asterisk are required.

A few sentences is enough — we'll ask follow-up questions.

We use your details only to reply. See our privacy policy.
Frequently asked questions

HIPAA Compliant Chatbot Questions

Talk to the specialist who would scope the work — not a call-centre script.

Ask us directly
Is there a HIPAA compliant chatbot for websites?

No chatbot is compliant on its own, but a chatbot deployment can be. Every vendor that sees conversations signs a BAA, PHI is collected only after sign-in, transcripts are encrypted and access-logged, trackers stay out of the chat, and the deployment appears in your risk analysis. We build to that standard on BAA-covered cloud services.

Is ChatGPT HIPAA compliant?

Only specific OpenAI offerings come with a BAA: sales-managed ChatGPT Enterprise and Edu accounts, an in-product flow for eligible clinicians using ChatGPT for Clinicians, and most API services after case-by-case review. ChatGPT Business is excluded. For a website chatbot, the OpenAI API or Azure OpenAI under Microsoft's BAA are the practical routes.

Must our chat vendor sign a BAA?

If the chat platform receives, stores or transmits PHI for you, yes. That includes widgets where visitors type symptoms or appointment details on a provider's site. If the vendor will not sign, limit the widget to general questions, tell visitors not to share health information, and route anything personal to a covered channel.

What is a HIPAA compliant chat API?

It is a chat or messaging API whose provider signs a BAA covering that specific API and lets you control encryption, retention and access logging. Scope matters, because vendors commonly cover some products and exclude others. We check the eligible product list and your account tier before any PHI passes through.

Can a chatbot on our public website collect symptoms?

It can, but it is then handling PHI. OCR's tracking guidance says symptoms entered into a tool on an unauthenticated page can be identifiable health information, so the chat vendor needs a BAA and no tracking code may read that frame. A safer design keeps the public bot general and moves symptom intake behind sign-in.

Can a HIPAA compliant chatbot give medical advice?

We design bots that do not diagnose or recommend treatment. They answer from approved content, decline clinical judgment calls, show emergency instructions for urgent phrases and hand off to staff. California also requires providers using generative AI for clinical patient messages to disclose it and explain how to reach a human, unless a licensed provider reviews them.

How long should chatbot transcripts be kept?

HIPAA sets no single retention period for transcripts. Security Rule documentation must be kept six years, and transcripts used to make decisions about patients may form part of the designated record set, which state medical record laws also govern. Decide retention on purpose, store transcripts encrypted and log who reads them.

Can the chatbot book appointments?

Yes, once the patient is identified. We connect the bot to your scheduling or EHR system through its API or FHIR interfaces, confirm identity before showing existing appointments, and keep the reason for visit out of analytics. Follow-up reminders can use the patterns on our HIPAA compliant SMS API page.